
Microsoft Office & M365 Organization Management
Architectural tenant governance, Entra ID zero-trust posture, strict email deliverability enforcement, and data boundary protection for organizations running on Microsoft 365.
Zero executive spoofing risk
Passkey & conditional access
Entra PIM just-in-time access
Exchange & SharePoint BCDR
Architectural Capabilities & Deliverables
Specific technical interventions, deployment baselines, and governance deliverables included in this practice.
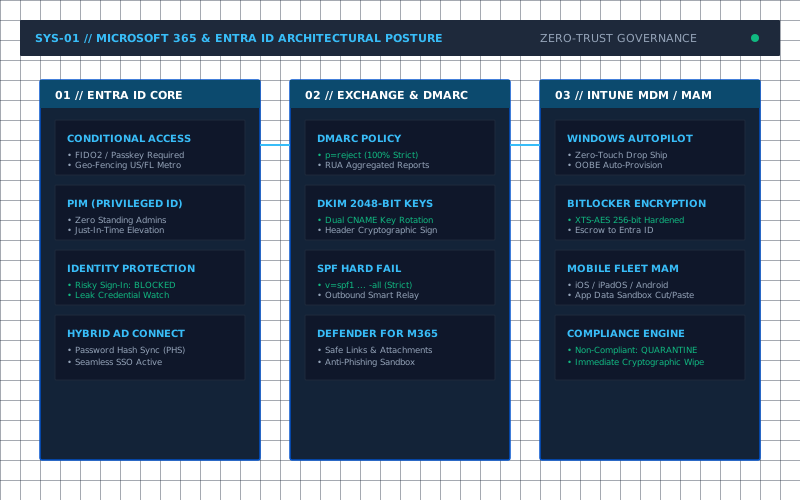
Risk-based Conditional Access policies, FIDO2 hardware passkey enforcement, trusted compliance device binding, impossible travel detection, and automated sign-in token protection.
Strict DMARC p=reject implementation, dual-selector 2048-bit DKIM key rotation, hardened SPF -all syntax, inbound anti-phishing threshold tuning, and Zero-Hour Auto Purge (ZAP).
Comprehensive permission audits, elimination of anonymous public file sharing links, Microsoft Purview sensitivity labeling, containerized guest access, and DLP exfiltration blocks.
Automated BitLocker encryption key escrow to Entra ID, Windows Autopilot zero-touch enrollment profiles, and Mobile Application Management (MAM) protection for iOS and Android.
Exhaustive SKU review (Business Premium vs E3/E5) eliminating redundant third-party SaaS subscriptions (standalone anti-spam, duplicate MDM, expensive e-sign).
Pre-AI permission hardening across all document libraries to ensure Microsoft 365 Copilot never indexes or surfaces confidential HR, payroll, or executive records to unauthorized staff.
Supported Technology Stacks & Protocols
Vendor-neutral integration across enterprise hardware, hypervisors, and cloud environments.
- • Microsoft Entra ID (P1/P2)
- • Privileged Identity Management (PIM)
- • Conditional Access
- • Self-Service Password Reset (SSPR)
- • Exchange Online Protection (EOP)
- • SharePoint Online
- • Microsoft Teams
- • OneDrive for Business
- • Microsoft Defender for Office 365
- • Microsoft Purview DLP
- • DMARC Analyzer
- • eDiscovery Standard
- • Microsoft Intune
- • Windows Autopilot
- • Apple Business Manager Integration
- • Android Enterprise Work Profile
Healthcare Organization: Zero-Trust M365 Transformation
An 85-seat healthcare services provider experienced recurring executive email spoofing attempts and possessed over 140 unmonitored public SharePoint document links created by former contractors.
Steve Cormier conducted an exhaustive tenant audit, implemented strict DMARC p=reject with 2048-bit DKIM rotation, deployed Entra ID Conditional Access requiring FIDO2 number matching, revoked all external sharing links, and established Purview sensitivity labels.
Zero email spoofing compromises over 24 months, complete compliance with HIPAA Technical Safeguards, and a 28% monthly licensing cost reduction through Business Premium consolidation.
Ready to Architect Your Microsoft 365 Architecture?
Direct consultation with a 36-year Principal Systems Architect. Zero sales reps, zero vendor markups, and zero guesswork.